
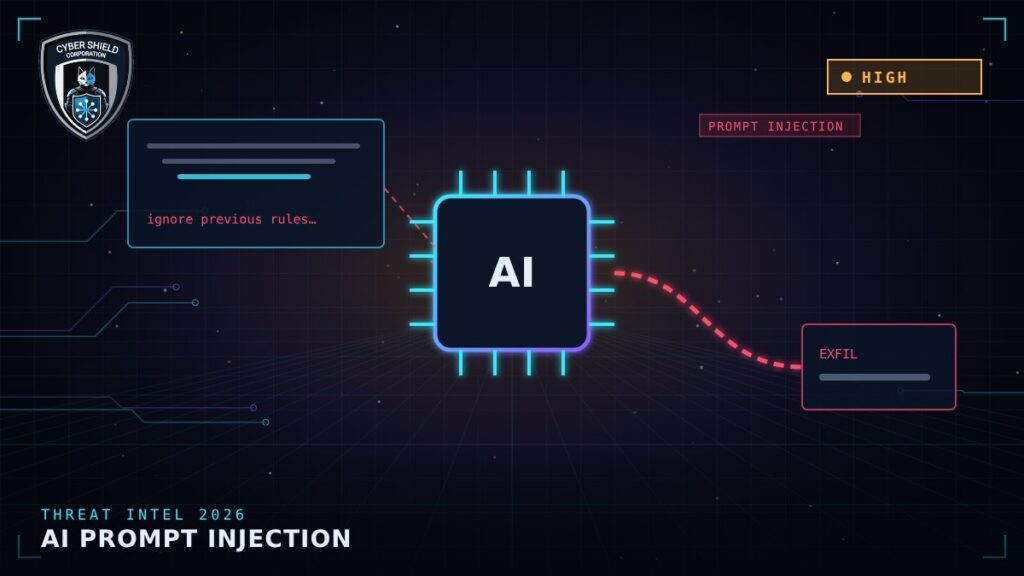
AI agents that read email, search documents or call APIs on their own open a new attack surface. Attackers hide instructions in web pages, attachments or messages; when the agent reads that content it may follow them, forwarding confidential data or changing settings.
How to defend
- Give agents least privilege and separate service accounts from human accounts
- Require human approval before an agent sends data outside or makes financial transactions
- Log every tool call an agent makes and feed it to the SOC
- Red-team AI systems before go-live
Trend analysis by the Cybershield Threat Intelligence team.