
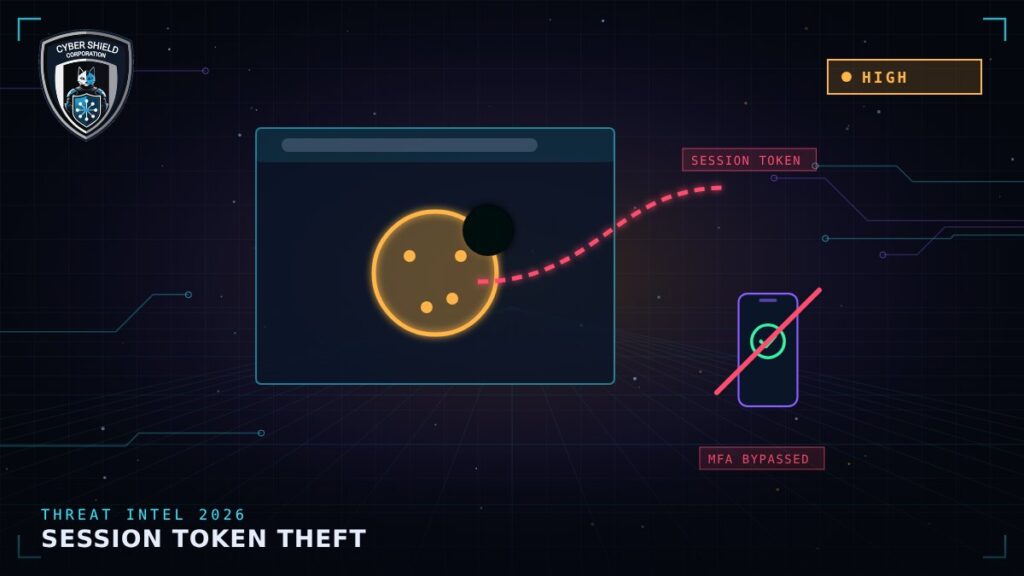
Attackers no longer need your password. If they steal the session cookie issued after login and MFA, they can use email, file shares and SaaS as that user immediately.
How to defend
- Adopt phishing-resistant MFA such as passkeys or FIDO2 keys
- Use conditional access to bind sessions to managed devices
- Shorten session lifetimes and revoke on suspicious behaviour
- Run EDR to catch infostealers on user machines
Trend analysis by the Cybershield Threat Intelligence team.